
Blog: Art-Kubed
Your Customers Are Bringing Their Own Agents: Operant Personal Agent Defense Now Enables Them Securely
Poppy defines how a personal agent proves who it is and who it acts for. It does not decide which agents a company should accept, or whether a given action makes sense for what the person actually asked. That's where Operant Personal Agent Defense comes in.
For years, companies built their digital front doors for two kinds of visitors: people in browsers, and partner systems with API keys. A third visitor has just arrived. It is a personal agent acting for one customer, and it wants to return a jacket, rebook a cancelled flight, or sit in on a support chat.
Poppy, the Personal Agent Protocol, is the company-side interface for exactly this. A personal agent presents a signed Session that says which agent it is and which person it represents (as a pseudonymous User ID that is meaningful only at your company). From there it can start a conversation with your company agent, call your MCP tools and APIs, and even join a browser session on your website.
Personal agents are no longer a thought experiment. Poppy already has backing from Muse and Shopify, and live implementations are appearing in the wild. The authoritative 1.0 specification is still a draft, which is a good reason to put your defenses in one place that can track it.
Where the protocol stops
Poppy is the identity and Session envelope. It complements commerce and payment protocols such as UCP, AP2, x402 and MPP rather than replacing them. And it is deliberately silent on one question that every company must answer: which agents do we accept?
That decision, along with every decision that follows it, belongs to the company. A valid Poppy Session proves an agent's identity. It does not tell you whether this agent should be admitted, whether this tool call matches what the customer asked for, or whether the data about to leave your systems should leave at all.
Those decisions must happen request by request, before anything is forwarded and again before anything is returned.
Two ways to get personal agents wrong
The first is letting too much through.
Imagine a customer's agent that opens a conversation to return a jacket. The Session is valid, the customer is signed in, and the merchant's OAuth server has issued a token with the right scopes. Midway through, the agent is nudged by injected content on a page it read, and it starts calling a member-profile tool and then a business-upgrade payment link. Every credential is genuine. Protocol checks alone see nothing wrong.
We think of this as intent drift across channels: a legitimately authenticated agent whose actions have quietly left the task the customer gave it. The same drift can happen with no attacker at all, through a confused agent, a retry loop, or an over-eager tool choice. The damage is the same either way: data or dollars moving for a purpose nobody approved.
The second failure is blocking too much.
If your answer to personal agents is a blanket block, your customers' favorite assistant simply stops working with you. If your answer is a human approval on every call, the autonomy that made the agent useful disappears. Teams that face that choice tend to switch security off entirely.
Personal agents need both at once: a front door that welcomes them and does the routine work without friction, and one that closes the moment they stray from the task.
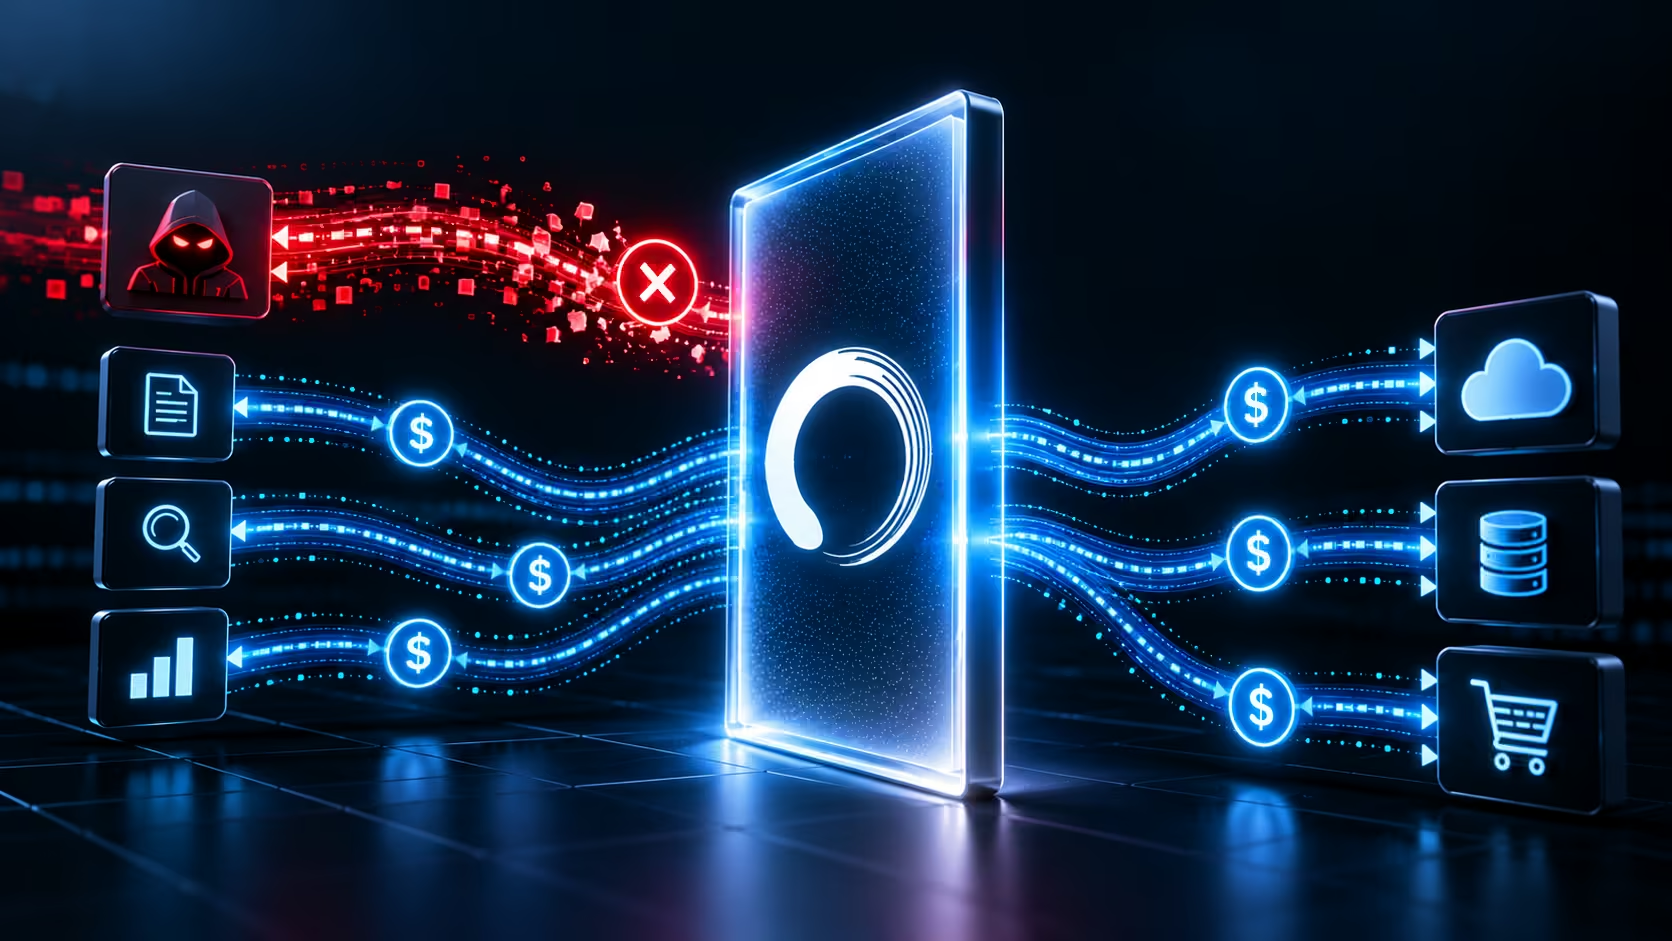
Every personal agent reaches your conversation endpoint, MCP and OpenAPI services, and website through one edge, which verifies, scopes, approves, and scans before anything moves.
Protection at the company's edge
Operant Personal Agent Defense, built on Poppy 1.0, puts a single, verified edge in front of the company's conversation endpoint, MCP servers, OpenAPI operations, and joined browser sessions. It follows the guidance in the Poppy company guide: verify the Session once at the gateway, then pass the trusted client ID, Session, user ID, and agent ID downstream.
The gateway stays at the merchant's edge. It does not become a personal agent, and it does not become your OAuth server.
Verified identity, never display names
Before anything runs, Operant confirms the agent is who it claims to be and that its request is genuine, current, and meant for your company. If your customer is signed in, it also confirms their access is tied to this exact Session. If any check fails, the request stops. It never falls back to anonymous access.
You choose which agents come in
Operant admits agents by verified identity, never by the name they give themselves, so a lookalike can't borrow a trusted agent's access. Set your stance for agents you trust, agents you block, and agents you have never seen. Turned-away agents get a clear refusal, and anonymous visitors can still browse your catalog while account features wait for sign-in.
Operation entitlements
For each admitted agent, you decide which MCP tools and OpenAPI operations it may call, and which of them require a signed-in customer, specific scopes, task context, or an explicit approval. These rules narrow what is already allowed; they never grant more. If a policy is missing, invalid, or unavailable, the answer is deny. Your OAuth server remains the authority on scopes. Operant does not invent scope decisions for a token it cannot read.
Task-aware enforcement across channels
The first message a personal agent sends in a conversation is the task narrative. Operant stores it as the Session's task scope, and the Semantic Firewall evaluates every later message, tool call, and company-agent action in that Session against it. It is the same real-time, intent-based protection we described in the Semantic Firewall launch post, now applied to personal agents. A refund conversation that suddenly wants a payment link gets stopped, whether it arrives as a chat message, an MCP call, an API request, or a browser action.
We are honest about what this is: the narrative is the agent's assertion, not cryptographic proof of the customer's words, so Operant audits it as such. Task scope expires with the Session and is never silently carried to a new one. When a high-risk tool requires context and none exists, the request fails closed.
Data protection on the way out
Every result headed back to the agent passes through Operant's response scanning, with redaction or blocking applied by the agent's verified identity. Sensitive data, secrets, prompt injection, and hidden text are handled by the same Operant controls you already use for other agents. Poppy identity changes who is asking, not what a payload is, so nothing about your existing scanner configuration needs to change.
Approvals that cannot be replayed
For consequential actions such as an exchange, a fare difference, or an upgrade purchase, Operant enforces Poppy Operations v3 approvals. An approval is accepted only for the same owner, revision, and terms, and executes at most once, with replay-safe audit state. Where an operation is also a payment, Operant's existing agentic commerce controls for destination and budget apply on top.
Bring your OpenAPI, skip the Poppy work
Most companies will not rebuild their stack to speak Poppy, and they shouldn't have to. If you already describe your services with OpenAPI, Operant compiles those operations into governed tools and serves them to personal agents behind the same verified edge, as MCP tools over Streamable HTTP and as direct HTTP calls on the API paths you already advertise.
- Your OpenAPI contract stays the source of truth. Operant resolves only operations compiled from it, forwards the caller credentials you declare, and checks targets, redirects, response size, status, and content type on every call.
- Full protection, no extra integration. Poppy verification, agent admission, task scope, response scanning, and approvals apply to each operation exactly as they do for a native MCP server.
- A validated poppy.json for your domain. Operant supplies the document and you publish it on your own host, because a Poppy document speaks only for the host that serves it.
- Nothing moves. Your OAuth server, website, and business APIs stay exactly where they are.
Your services can welcome personal agents today, and your teams can adopt native Poppy, MCP, or both on their own schedule.
Deep observability into agent behavior
Stopping bad actions is one benefit of standing at the edge. The other is seeing what personal agents actually do at your company, a view most teams have never had. Every request, allowed or refused, produces telemetry that follows one agent through one Session across conversation, API, and browser channels:
- Who: the verified agent client ID, the pseudonymous user ID, the Session, and the sign-in and scope posture.
- What and where: the channel, conversation, tool or operation, and who authored each message (personal agent, user, company agent, or company human).
- Why it was allowed or stopped: the policy decision, the task scope it was measured against, approvals requested and granted, and what was redacted or blocked on the way out.
That turns open questions into answers: which agents are visiting, which tools they favor, where conversations drift from their opening task, and which approvals are granted or abandoned. Everything is keyed on verified identity, never on an unverified claim, and the task narrative is recorded as what it is, an agent-asserted task. It is the same native agentic telemetry that you own across the rest of the Operant platform, so personal agents show up beside every other agent you secure.
Three journeys, one Session
The real world rarely uses one channel at a time, so Operant is built around the three scenarios in the Poppy specification:
- Returning a jacket. The agent starts a conversation, your company agent asks for sign-in, and your OAuth server issues the token. Operant binds the token to the Session, scans the conversation and the order data that comes back, and requires an approval for the exact exchange before it runs once.
- Getting help on the website. The agent joins a browser session. The OAuth token stays out of the browser, your website's own Session cookie takes over, and website actions are tied to the same task. When a person at your company or the customer steps in, their messages keep human attribution.
- A disrupted flight. Search, rebooking calls, company-agent messages, and website actions all happen under one verified Session, and all are measured against the original disruption. The exact itinerary and fare difference need approval before anything executes.
One guard across an interlocking stack
Poppy is the identity layer. Commerce and payments ride alongside it: UCP for catalog, cart, and checkout, AP2 for signed purchase mandates, x402 and MPP for payment transport and settlement. Operant applies one policy model across all of them, so the rules follow the agent instead of the protocol. For every request, Operant asks:
- Is this agent verified, and is it one we admit?
- Is it allowed to use this tool or operation, signed in or out?
- Is the action consistent with the task the customer gave it?
- Does this action need an approval, and is it the exact one that was granted?
- Should this data leave, and in what form?
- If money moves, is the destination approved and the budget available?
The protocol handles identity and Session. Your merchant systems keep OAuth, your website, and your business APIs. Operant decides whether each step the agent takes should be allowed to happen.
Your customers get an agent. You keep the front door.
Book a demo to see Operant's Personal Agent Defense in action today!